Private APN security for 350,000 field SIMs
The General Directorate of Security (Emniyet Genel Müdürlüğü) connects field terminals and in-vehicle devices over a private APN with APNZone and ConnGuard.
Last updated:
350,000SIMs
General Directorate of Security (Emniyet Genel Müdürlüğü) · Scale
Source: NSS project record
- Customer
- General Directorate of Security (Emniyet Genel Müdürlüğü)
- Products used
- APNZone + ConnGuard NAC
The challenge
Securely connecting field terminals and in-vehicle devices, against SIM cloning and unauthorised device access.
The solution at a glance
The project
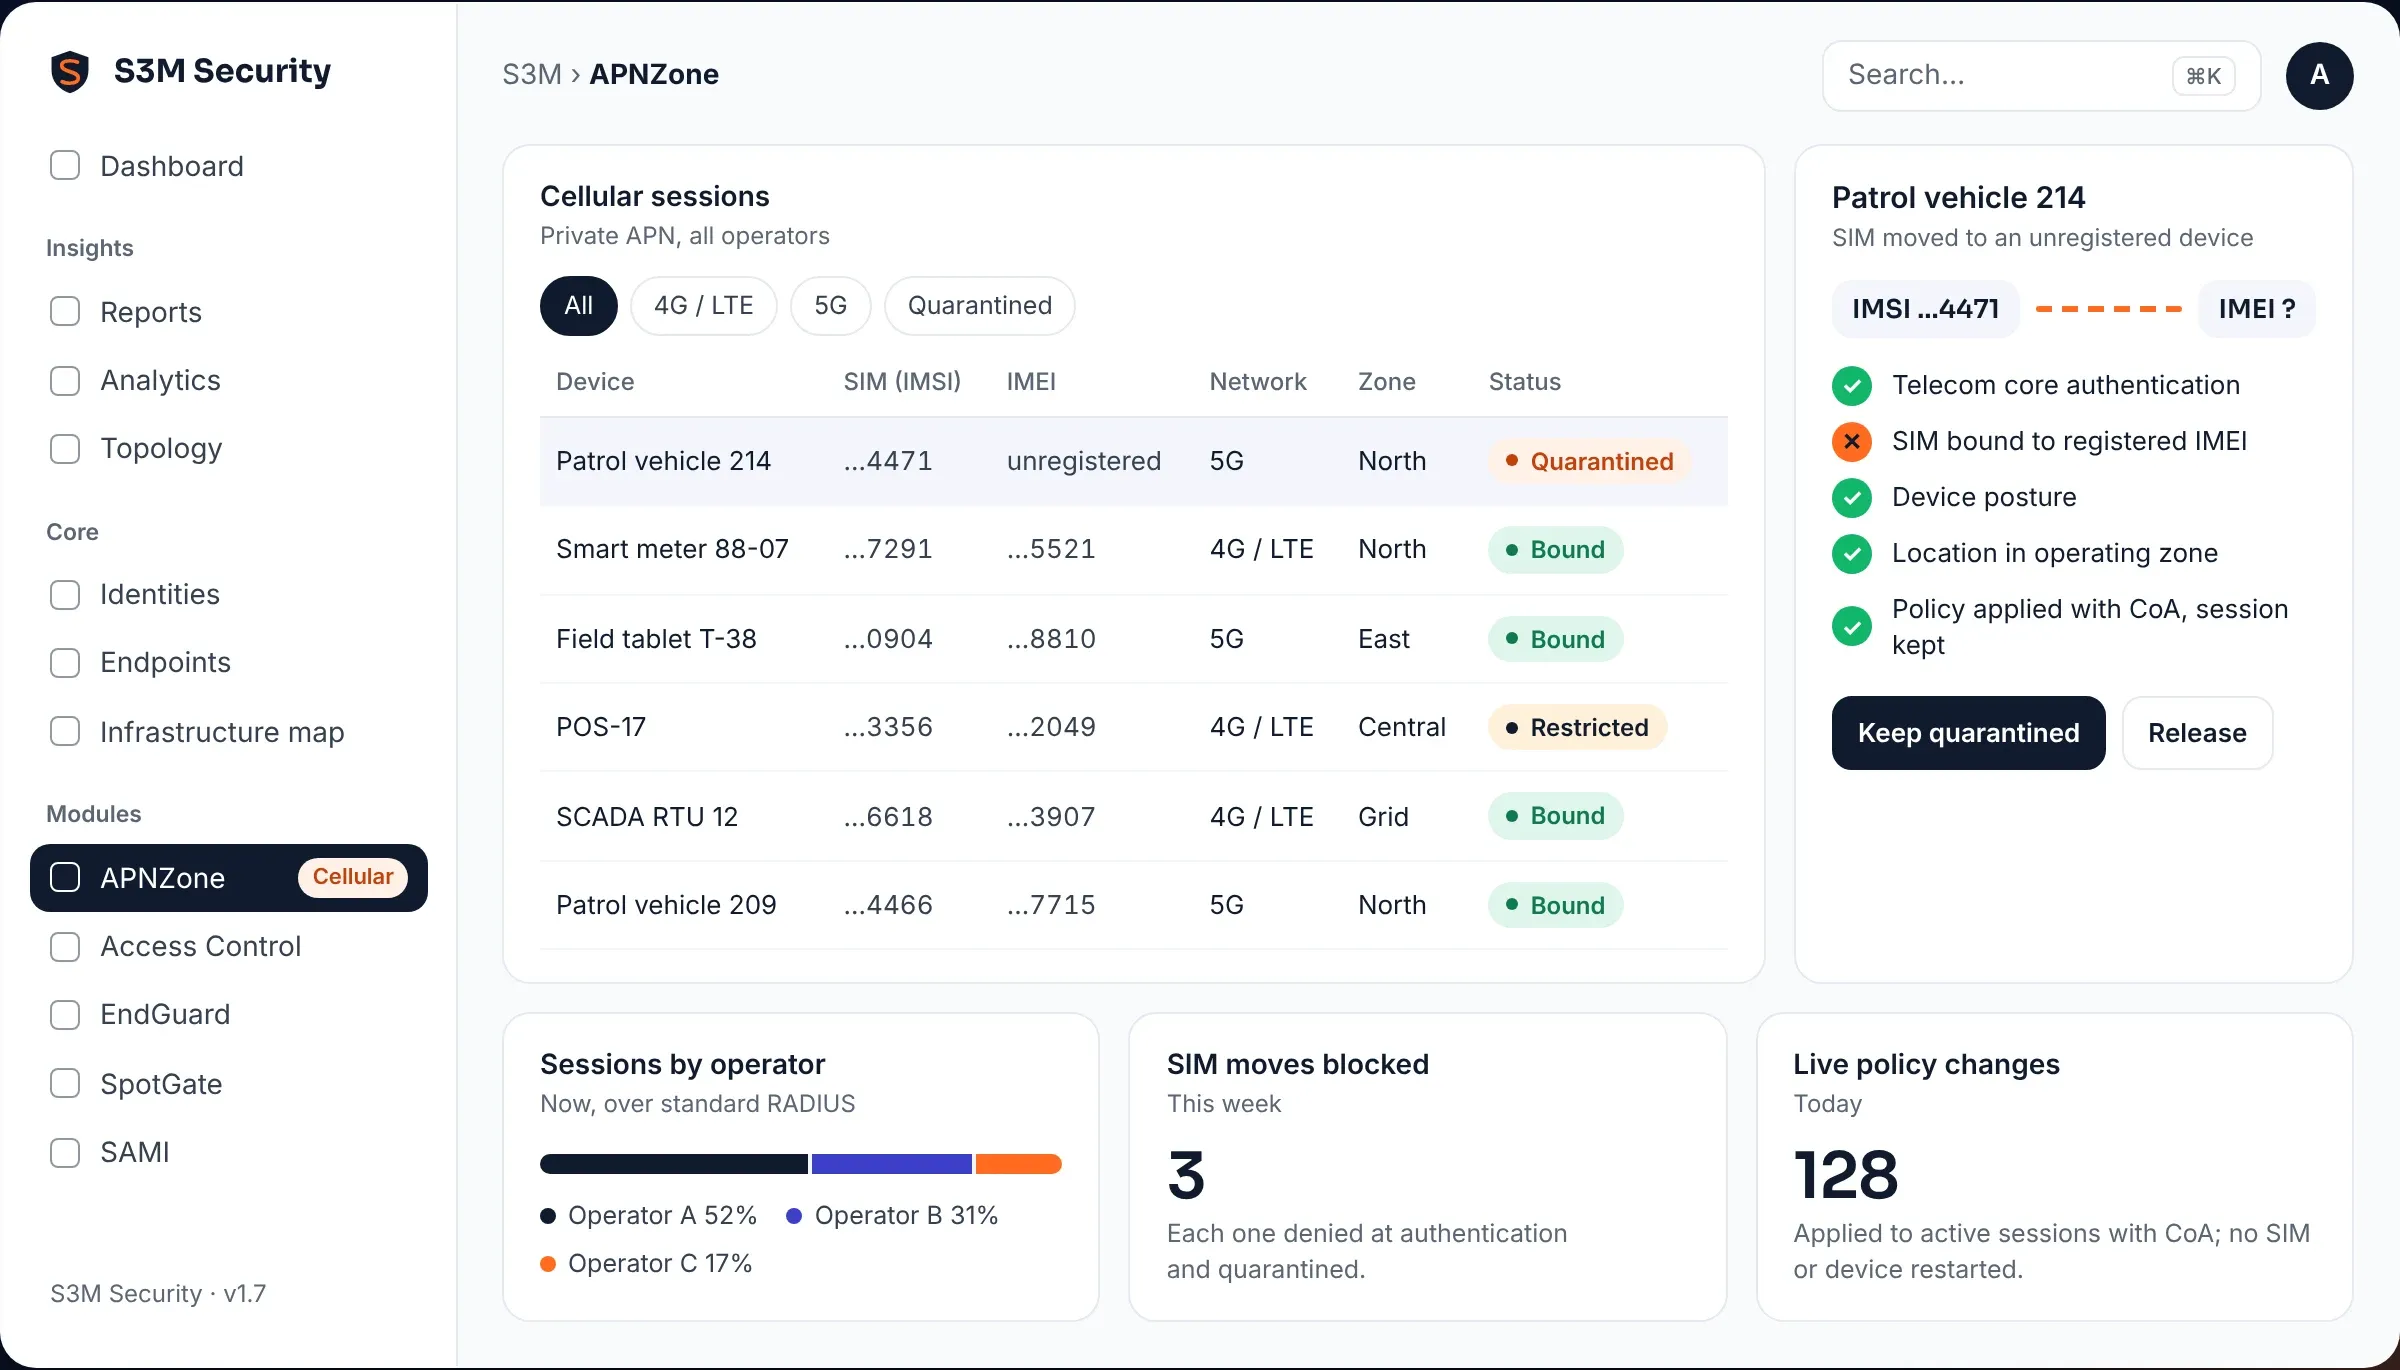
Vehicle terminals, mobile data terminals and handhelds of the General Directorate of Security (Emniyet Genel Müdürlüğü) connect over a private APN. Every SIM is bound to its registered device.
How it works
- SIM-to-device binding: APNZone pairs each SIM (IMSI) with the identity of its registered device (IMEI). If the SIM is moved to another device, the connection is refused at authentication.
- Off the public internet: Field devices stay on the private APN and are not visible from the public internet.
- Isolation from one console: A lost or stolen device can be cut off nationwide from a single console.
Products used
 APNZone(in Turkish)Zero Trust for private APN and cellular links: each SIM (IMSI) is bound to its device (IMEI), posture is checked and policy is applied live over the operator's RADIUS.
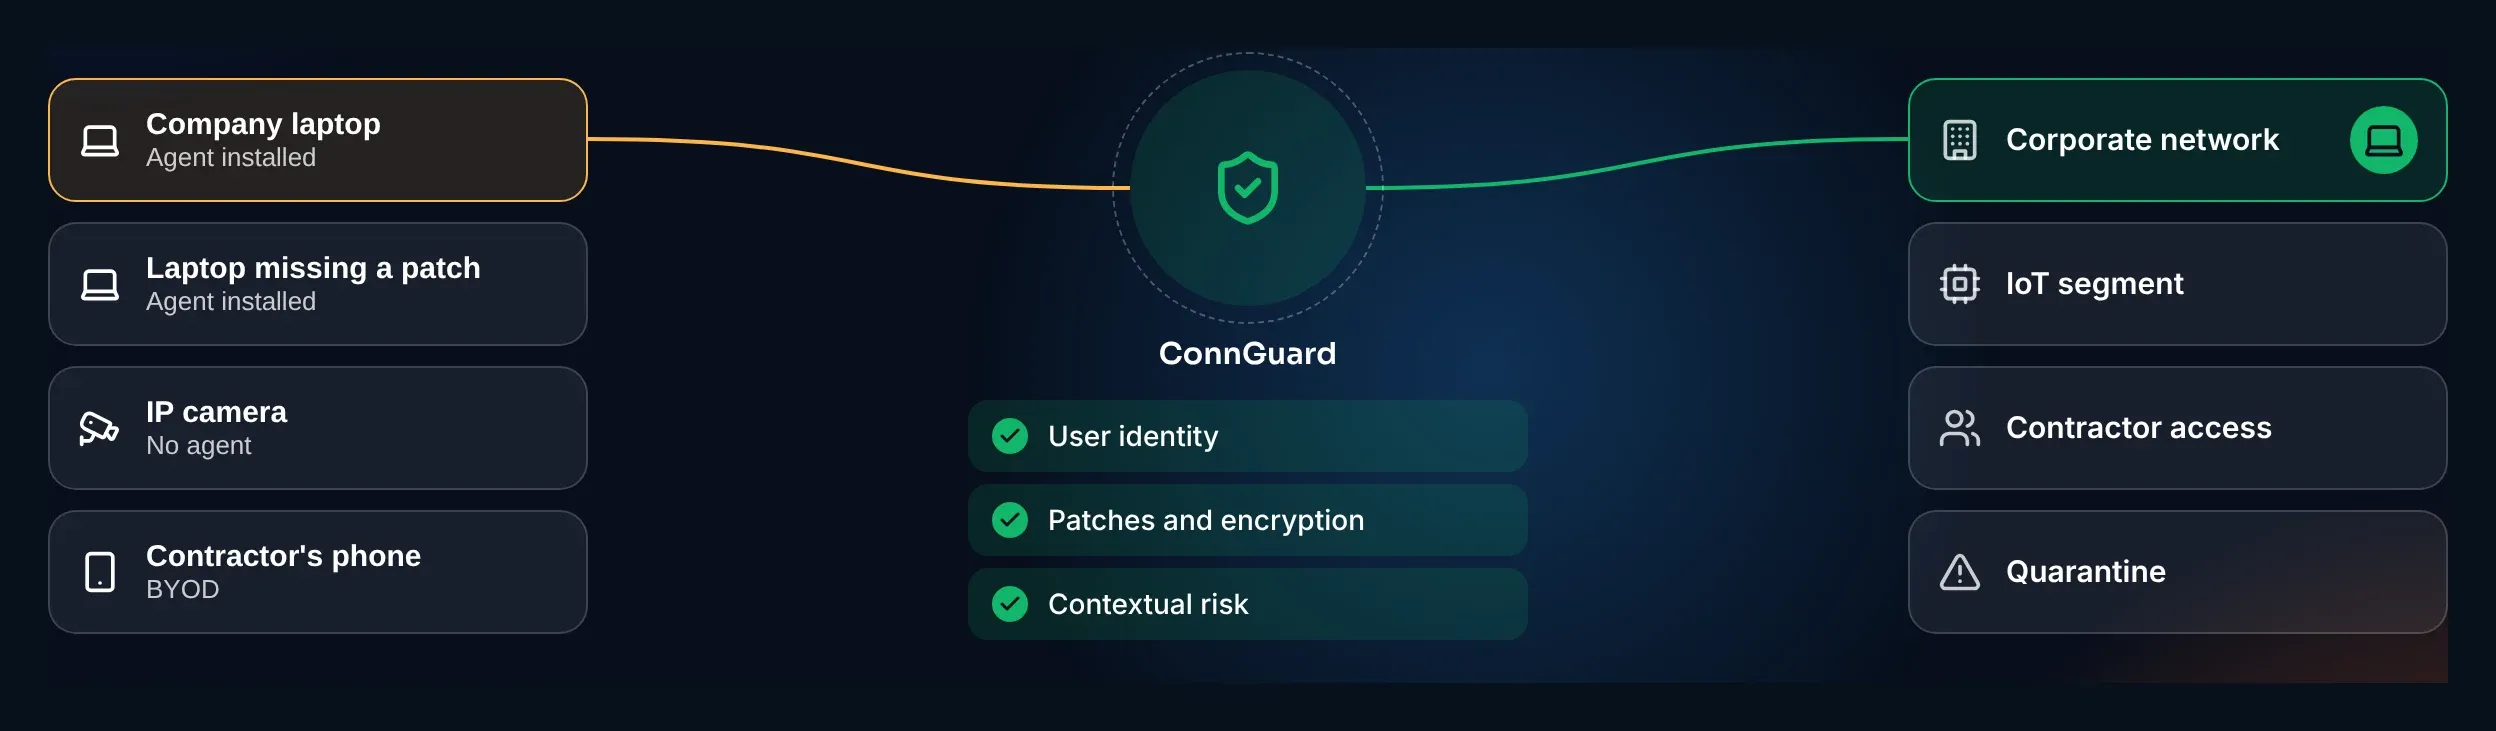
- ConnGuard NAC(in Turkish)Identity-based access control for wired, wireless and VPN networks, combining agent-based posture checks with agentless device profiling.
Next step
Let’s design the right architecture for you.
Our solution architect listens to your needs and proposes a roadmap that fits your existing infrastructure.
- Response within 24 hours
- or call +90 216 339 97 71
Request received
Thank you. Our expert will get back to you by e-mail or phone within 24 hours.
Reference:
For urgent matters: +90 216 339 97 71